Why Retired Technology Is Still a Security Risk—and How ITAD Closes the Gap
Practical guidance on secure technology retirement, chain of custody, data sanitization, asset recovery, and responsible recycling.
Retired does not mean harmless
When a laptop, server, storage array, phone, or network appliance reaches the end of its useful life, the business risk does not disappear. Retired technology may still contain customer records, employee information, credentials, intellectual property, financial data, system configurations, and access tokens. A device sitting in a storage room—or moving through an undocumented disposal channel—can remain a security exposure for months or years.
That is why secure IT asset disposition, commonly called ITAD, should be treated as an extension of information security and asset management rather than ordinary electronics recycling.
Where retirement projects commonly lose control
- Incomplete inventories: equipment leaves a site without a serial-level record.
- Broken custody: responsibility is unclear during staging, loading, transportation, or receiving.
- Unverified erasure: someone assumes a factory reset removed the data.
- Unhandled exceptions: failed, locked, or damaged drives are not quarantined and escalated.
- Unclear disposition: the organization cannot show whether an asset was reused, sold, destroyed, or recycled.
What a secure ITAD program should document
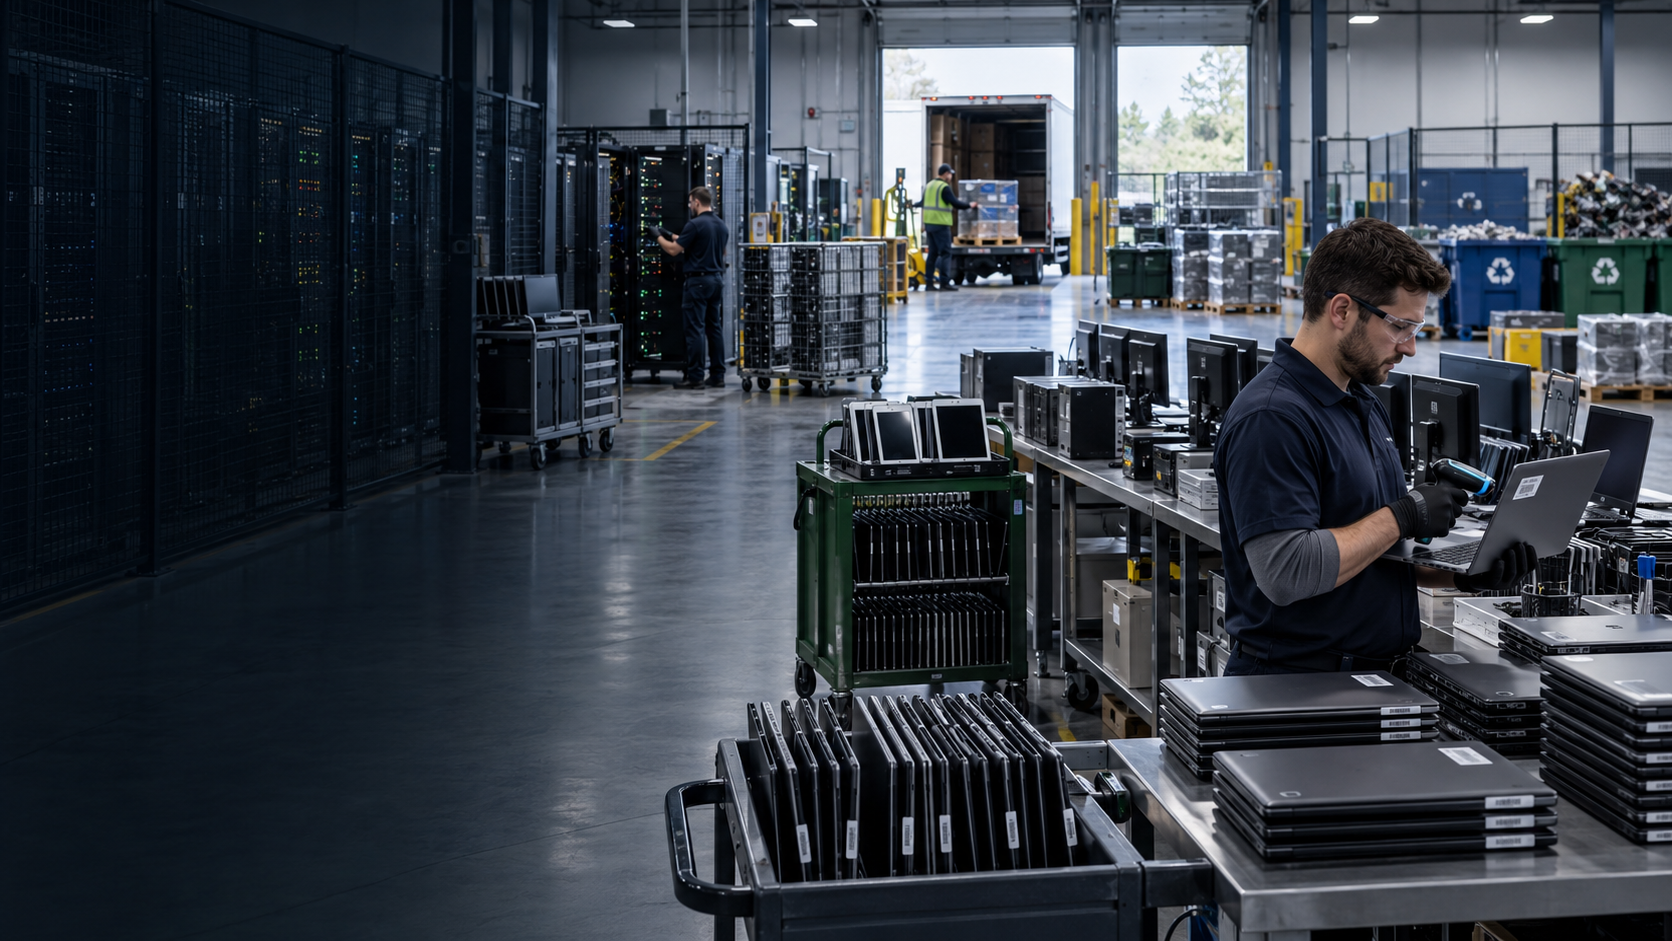
A controlled project begins before equipment moves. The customer and ITAD provider define locations, asset types, quantities, timing, security rules, resale eligibility, and required reporting. At pickup, custody is formally transferred and the shipment is connected to the customer, project, site, container, and authorized personnel.
After receiving, each asset should be reconciled to the manifest and associated with a unique tracking record. Data-bearing media must be identified separately so its sanitization outcome remains linked to the correct device.
Sanitization must produce evidence
Appropriate media can be securely erased using a verified Clear or Purge method aligned with NIST SP 800-88. Media that is failed, damaged, locked, or unsuitable for reuse may require physical destruction. The important point is not simply that an action occurred—it is that the method, result, device identifiers, exceptions, and final outcome are documented.
Security and asset recovery can work together
Good ITAD does not require every device to be destroyed. Once data risk has been resolved, reusable equipment can be tested, graded, refurbished, remarketed, redeployed, or harvested for parts. Recoverable value may help offset project costs when the ownership and value terms are agreed in advance.
Non-recoverable equipment should move to qualified downstream processors appropriate to the material and required disposition. Final reporting closes the loop by reconciling the original inventory with sanitization results, recovery outcomes, recycling paths, and exceptions.
The practical takeaway
If your organization cannot identify what left, who handled it, how data was addressed, and where each asset ultimately went, the retirement process has a control gap. A documented ITAD program turns that uncertain handoff into an auditable security process.
Turn the guidance into a secure ITAD plan.
Tell Slate Peak what you are retiring and we’ll help define pickup, data handling, value recovery, recycling, and reporting.